Complade provides SCC-accredited ISO/IEC 27001 and CyberSecure Canada audits and certification. We help organizations give customers, investors and boards independent assurance about information-security risk management. Published pricing, a documented audit process and one portal make certification easier to plan and follow.
01
Evidence buyers and boards can assess
The problem: Suppliers to regulated sectors must substantiate security claims. Growing companies, cooperatives and family offices also need to demonstrate risk management to stakeholders.
Our approach: SCC-accredited ISO/IEC 27001 certification provides independent assessment of your management system within a defined scope. It supports third-party risk management (TPRM), investor diligence and board oversight.
The problem: Unexplained criteria create uncertainty and findings that are difficult to understand.
Our approach: Review our published process, document requirements and evaluation resources before you begin. Auditors connect conclusions to applicable requirements and recorded evidence, using documented methods.
The problem: Without visible rates and inclusions, selecting a certification body consumes procurement and management time.
Our approach: See published pricing and calculate an estimate without a sales call. Your quotation confirms scope, audit time and charges before signing; taxes, travel and scope changes are identified separately.
The problem: A customer asks for your certification status before the audit is complete.
Our approach: Start your application and submit evidence online. Once the engagement is confirmed and the formal process is underway, Complade issues a same-day attestation letter confirming that certification is in progress. It is not a certificate or an assurance of conformity.
The problem: Scattered attachments, spreadsheets and email threads pull engineering and compliance teams away from their work.
Our approach: Use one audit portal for evidence, auditor discussions, findings and milestones. Asynchronous exchange keeps work moving between scheduled interviews and verification activities.
The problem: Stakeholders need a clear separation between implementing controls and independently assessing them.
Our approach: Complade does not provide implementation consulting or internal audits. Documented methods and conflict-of-interest controls govern audit delivery; a person independent of the audit team makes the certification decision.
Online application and evidence submission; letter on formal commencement.
Pricing
Comparing quotes without clear inclusions.
Public rates, online estimates and a quotation before signing.
Transparency
Discovering expectations during the audit.
Published process, requirements and evaluation resources.
Experience
Coordinating evidence across disconnected tools.
One portal for exchanges, findings and milestones.
Impartiality
Separating advice from certification decisions.
No implementation consulting; independent certification decisions.
Certification supports supplier diligence; it does not replace buyer-specific or regulatory requirements, including NIS 2 or DORA. Acceptance depends on the certificate, its scope and the applicable requirements. ENISA: supply chain security · DORA
Remote ISO 27001 audits for organizations worldwide.
Complade delivers ISO/IEC 27001 certification audits for organizations in Canada and internationally. Our portal brings applications, agreements, evidence and results together. Remote delivery is confirmed according to scope, locations and access to evidence.
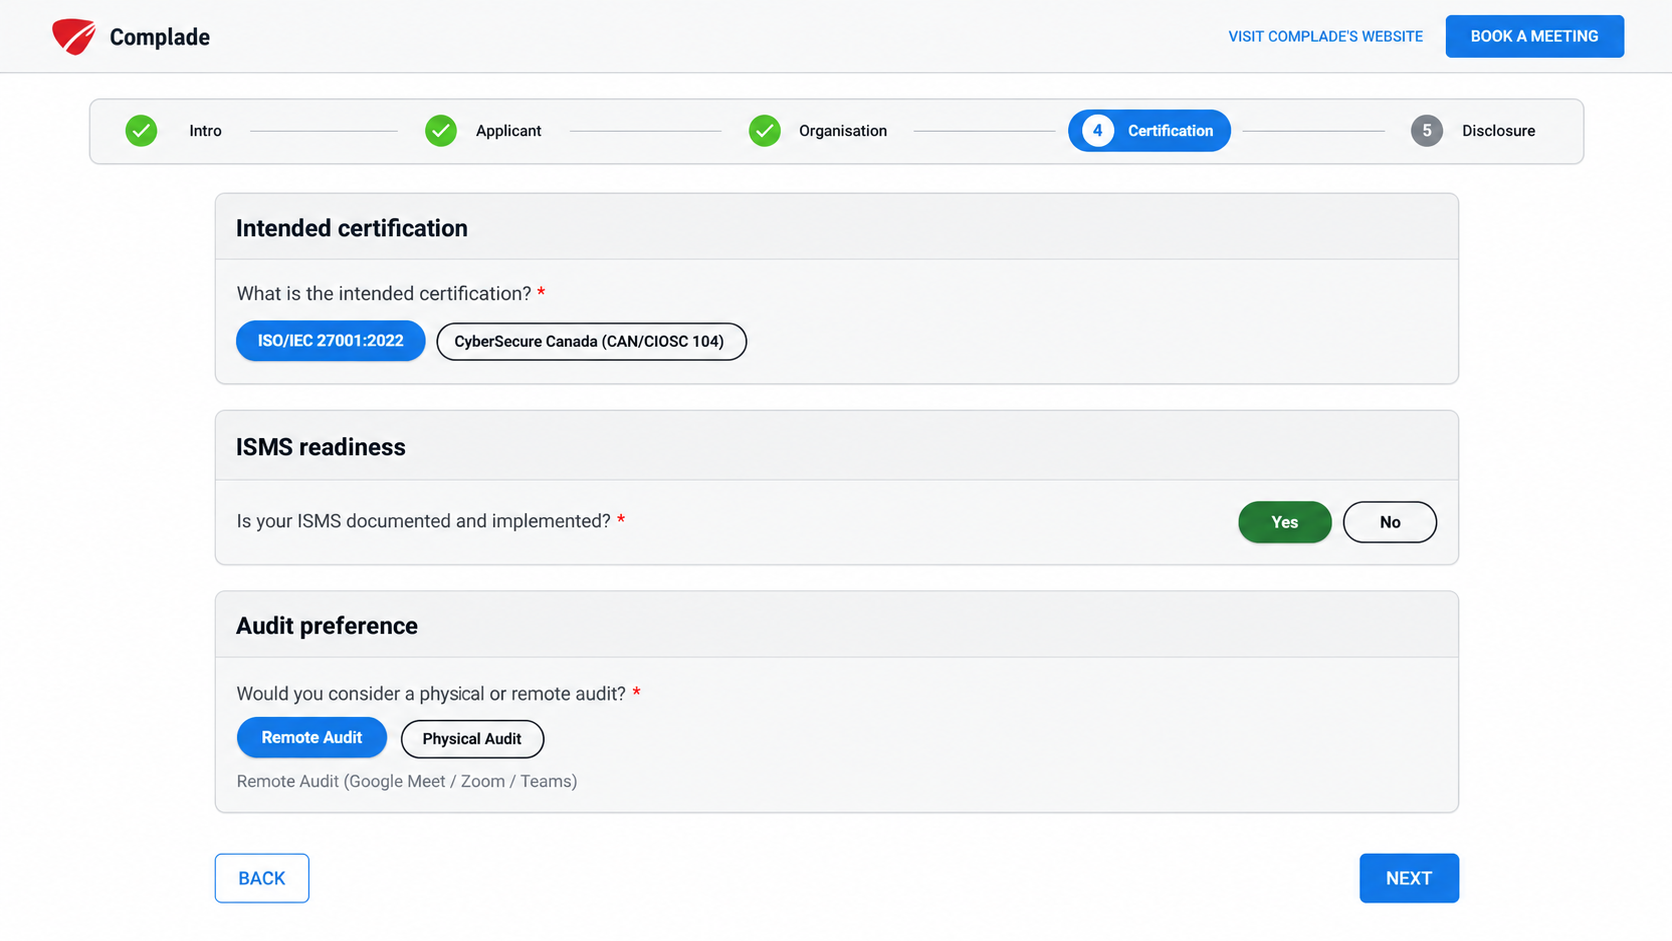
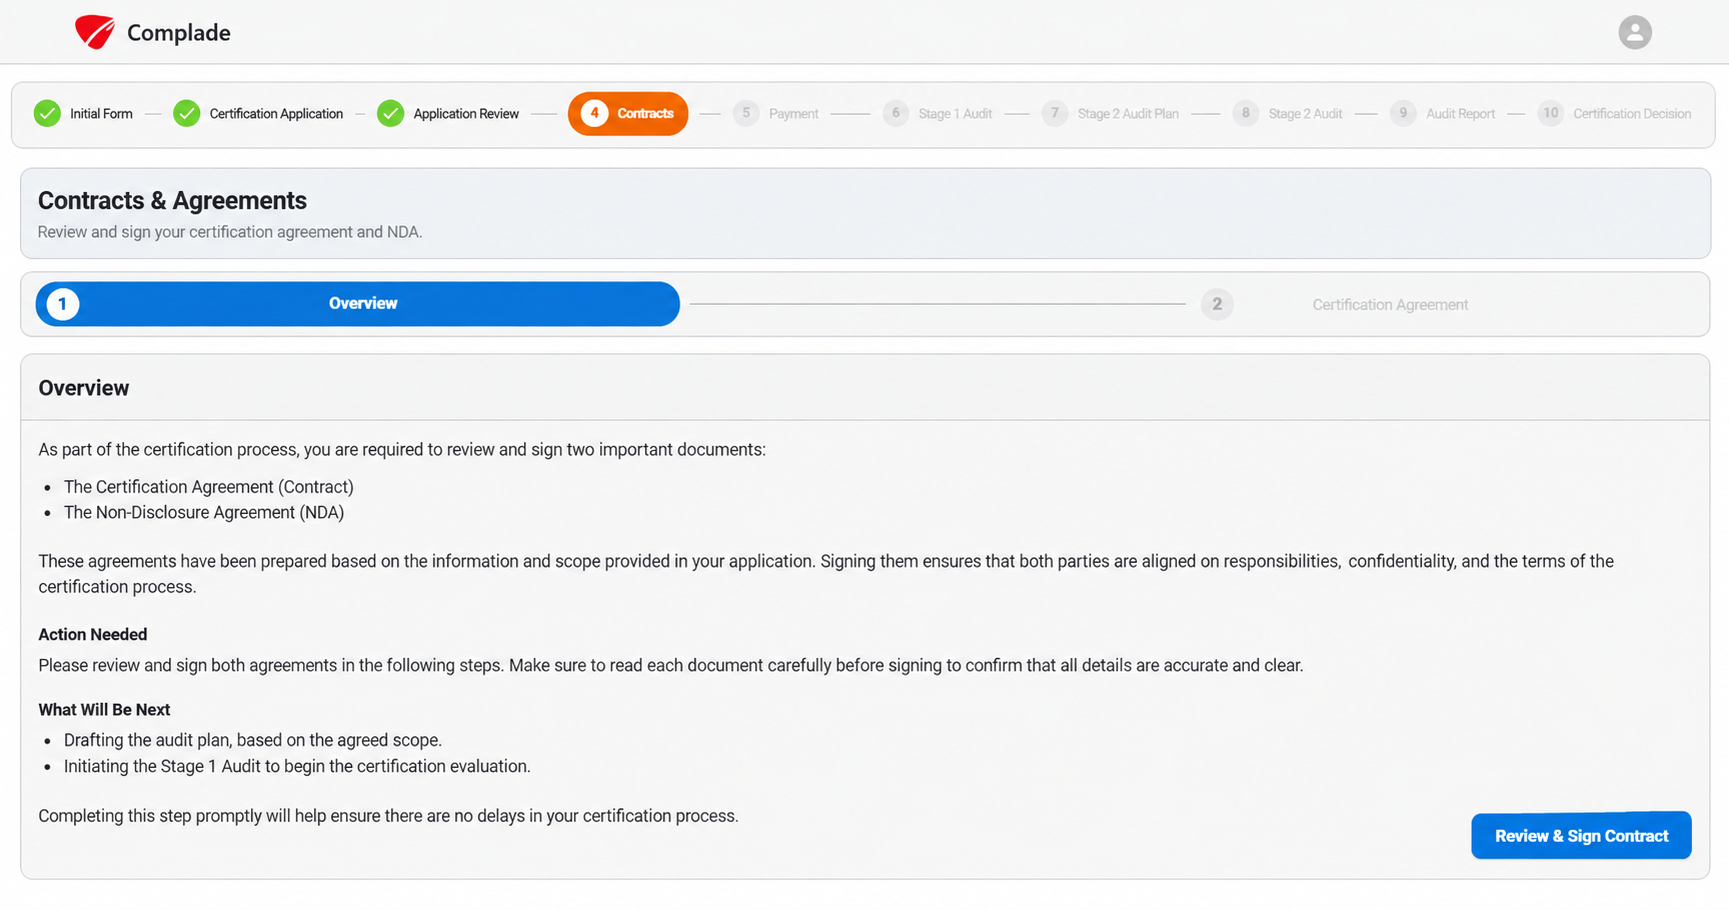
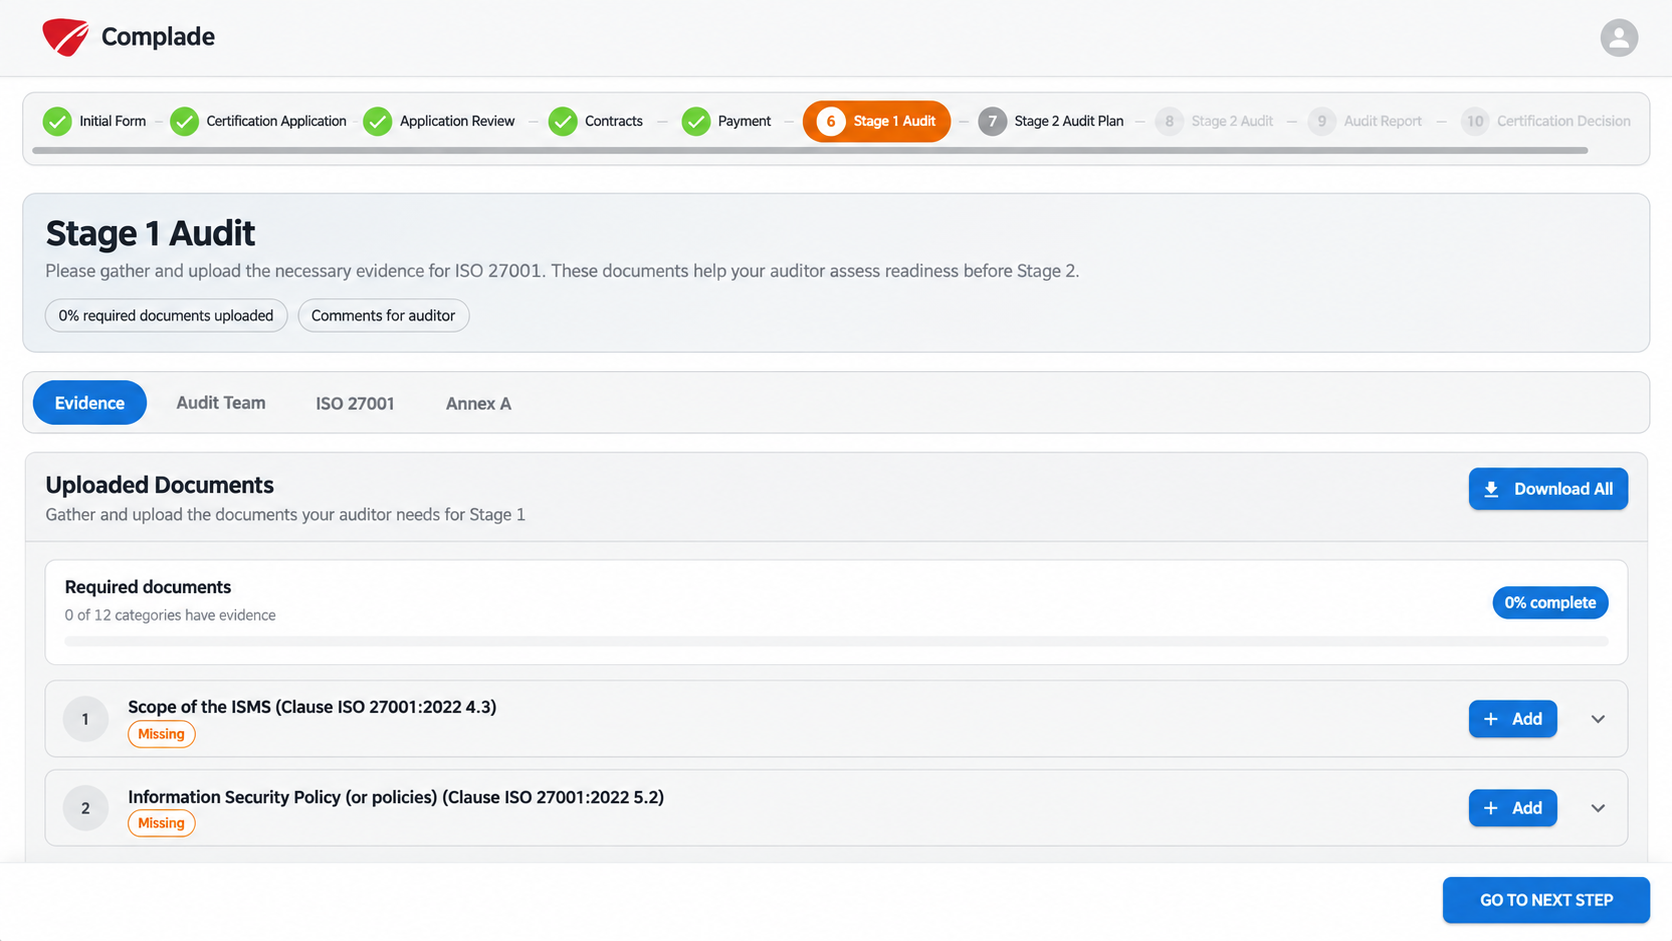
Apply free, review your quotation and agreements, then decide whether to sign. Meet your audit team and upload Stage 1 documents. Pay before the auditor begins reviewing them. Screenshots below use illustrative sample data.
Organizations of different sizes use Complade for independent assurance.
Complade works with organizations in aviation, financial services, healthcare, logistics, technology and community development. These clients describe their CyberSecure Canada certification experience.
Yes. The Standards Council of Canada accredits Complade for ISO/IEC 27001 and CyberSecure Canada certification. The official SCC directory and IAF CertSearch show Complade's current records.
Which certification should our organization choose?
ISO/IEC 27001 is an internationally recognized information security management system standard. CyberSecure Canada is Canada's national cybersecurity certification for eligible small and medium-sized organizations.
How much does certification cost?
Complade publishes planning estimates and their assumptions. The final quotation is confirmed after Complade reviews the application, certification scope and required audit time.
How long does certification take?
Timing depends on scope, readiness, document availability, auditor and client schedules, and the time required to resolve nonconformities. Complade publishes a fastest-case ISO 27001 planning scenario of about six weeks for an audit-ready small organization.
Can I speak with a Complade lead auditor before applying?
Yes. A lead auditor can explain the standard, process, scope factors, timing and published pricing. To protect impartiality, the auditor cannot design your system or tell you how to implement it.